Updated on July 14, 2026
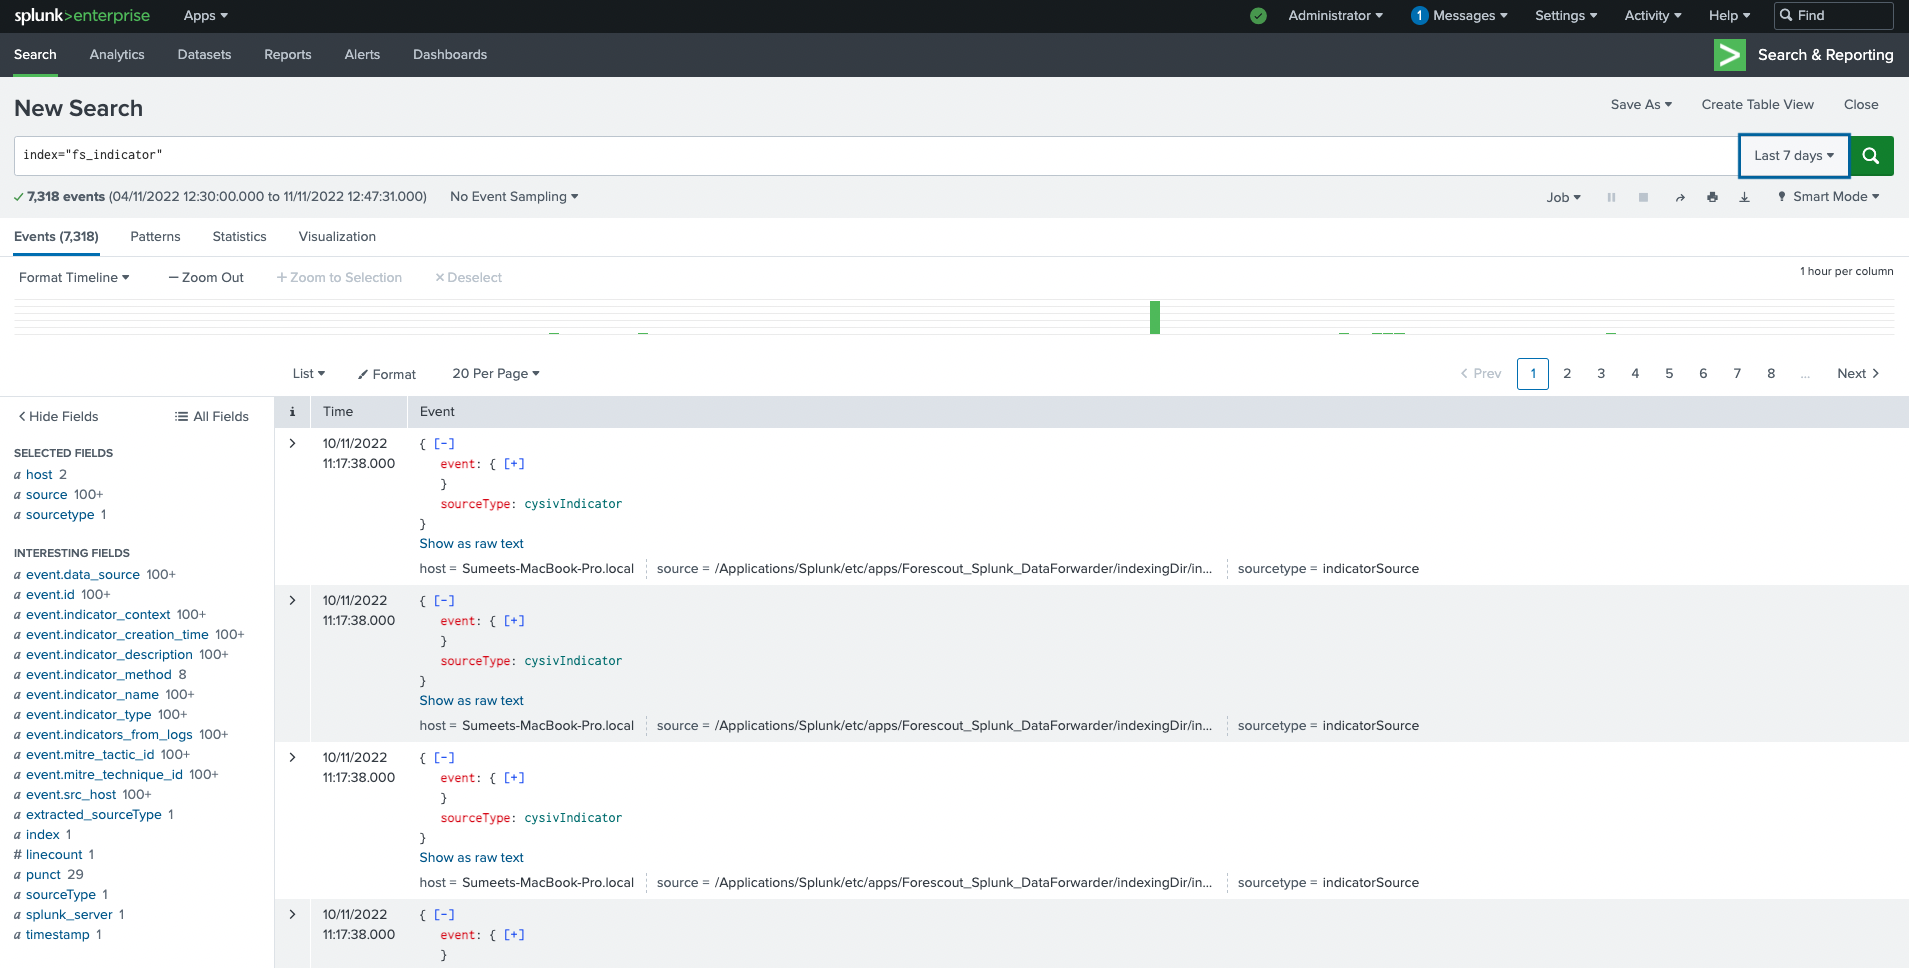
To verify that Splunk is receiving Indicator and Detection events, from Splunk home navigate to the Forescout Splunk DataForwarder application and use the search bar. Indicator data looks as follows:
On this page
minute read
 minute read