About the Flow Collector
The Flow Collector analyzes the traffic flows exported by network devices, such as switches, firewalls, and routers.
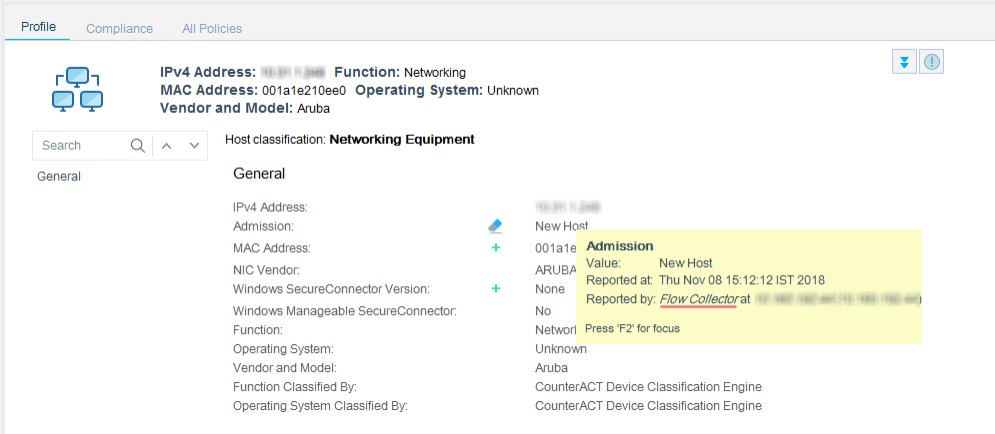
It reports flow session data that is used to resolve endpoint properties and that can be used to map visualized traffic patterns. The flow session data can also be used by other Forescout modules.
The Flow Collector is a component of the Forescout eyeSight (formerly Forescout Platform or CounterAct) Core Extensions Module.
The Flow Collector can detect endpoints or endpoint property values that the Forescout Packet Engine might not learn. This capability is relevant in large scale deployments where the Packet Engine is limited in its ability to detect activity in remote sites and branch offices. Use of the information reported by the Flow Collector improves visibility and speeds detection of new endpoints.
How It Works
The Flow Collector audits information from switches, routers and other networks devices that report traffic flow data. It filters the information and applies heuristic logic to enable the to report endpoint properties and session information.
Overlapping IP Address Support
The Flow Collector supports working with networks that use overlapping IP addresses. For details about enabling and configuring the ’s support of overlapping IP address use in an enterprise’s network, refer to the Forescout Working with Overlapping IP Addresses How-to Guide.
Deployment Scenarios
The is configured to collect traffic data in one of the following ways:
- Distributed Traffic Collection: Appliances analyze traffic for the endpoints they manage.
- Centralized Traffic Collection: One or more designated Appliances analyze the network traffic, and extract and distribute the endpoint properties and session information to the Appliances that manage the relevant endpoints.
 minute read