Creating Splunk indexes and installing the application package
This procedure provides medium-level guidance and assumes familiarity with Splunk™, Administrator-level knowledge and access, and is partly derived from vendor documentation located here and here:
- In Splunk Web, go to Settings > Indexes.
- On the Indexes page, click New Index.
- On the New Index page, in the Index Name field, enter a name for the new index. Keep the other default settings.
- Click Save.
- Navigate to Apps > Manage Apps > Install App From File > Choose File.
- Upload the
"Forescout_Splunk_DataForwarder-{SHA}.tar.gz" obtained from your Forescout
representative.
Note: In cases where the application has been previously installed, check the "Upgrade App" option after uploading the tar.gz file.
- Open a Command Line Interface (CLI) and navigate
to
"<splunk_home>/etc/apps/Forescout_Splunk_DataForwarder". - Install requirements using:
pip install -r requirements.txt - . Run a setup.py file from the same directory:
python setup.py --startTime "2022-09-03 13:00:00" --token
                        "<token_value>" --certificatePathForSetup
                        "<splunk_configured_cert>
where startTime is the date from which it will pull data and startTime should be in format of YYYY-MM-DD HH:MM:SS, token is Generic Query API token which is generated in step 1, and certificatePathForSetup is Splunk’s configured SSL certificate -
Note:If an SSL certificate for Splunk is not configured, please see Configure SSL Certificates for Splunk Management Port). Make sure to accept the EULA License and provide Splunk credentials with the management port URL for which the SSL certification is configured.
For help with configuration settings type"python setup.py -h"in the CLI. - In Splunk Web, go to Settings > Data Inputs > Scripts.
Two scripts from the Forescout Splunk DataForwarder application should be shown:
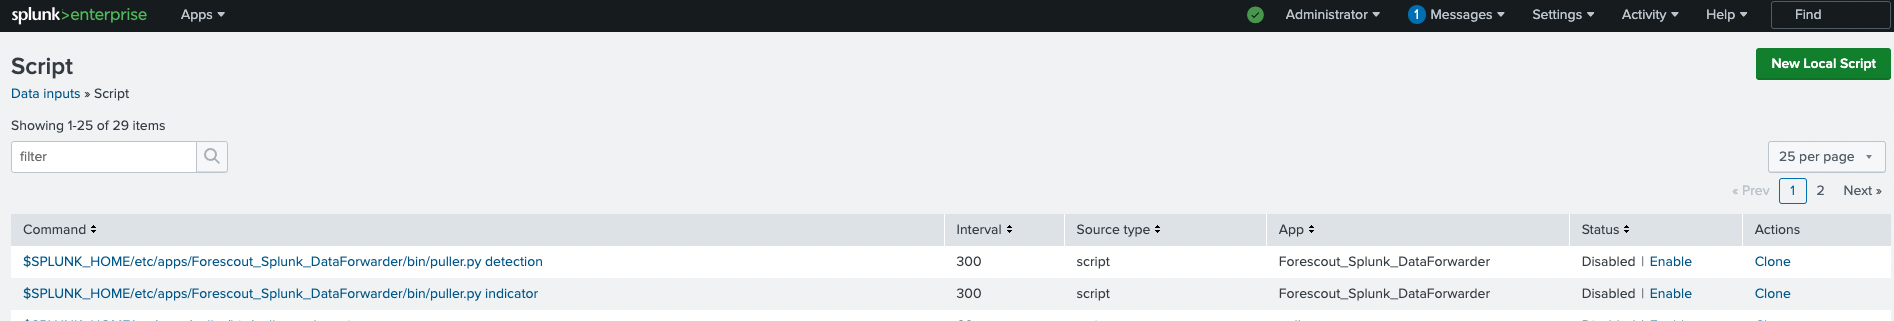
- Click Enable to start pulling data for Indicators and Detections.
Next, see Verifying that Splunk is receiving data.
 minute read